Claude BugHunter: The 83-Skill Pack that Turns Claude Code into a Senior Bug HunterClaude BugHunter:把 Claude Code 变成资深漏洞猎手的 83 技能包
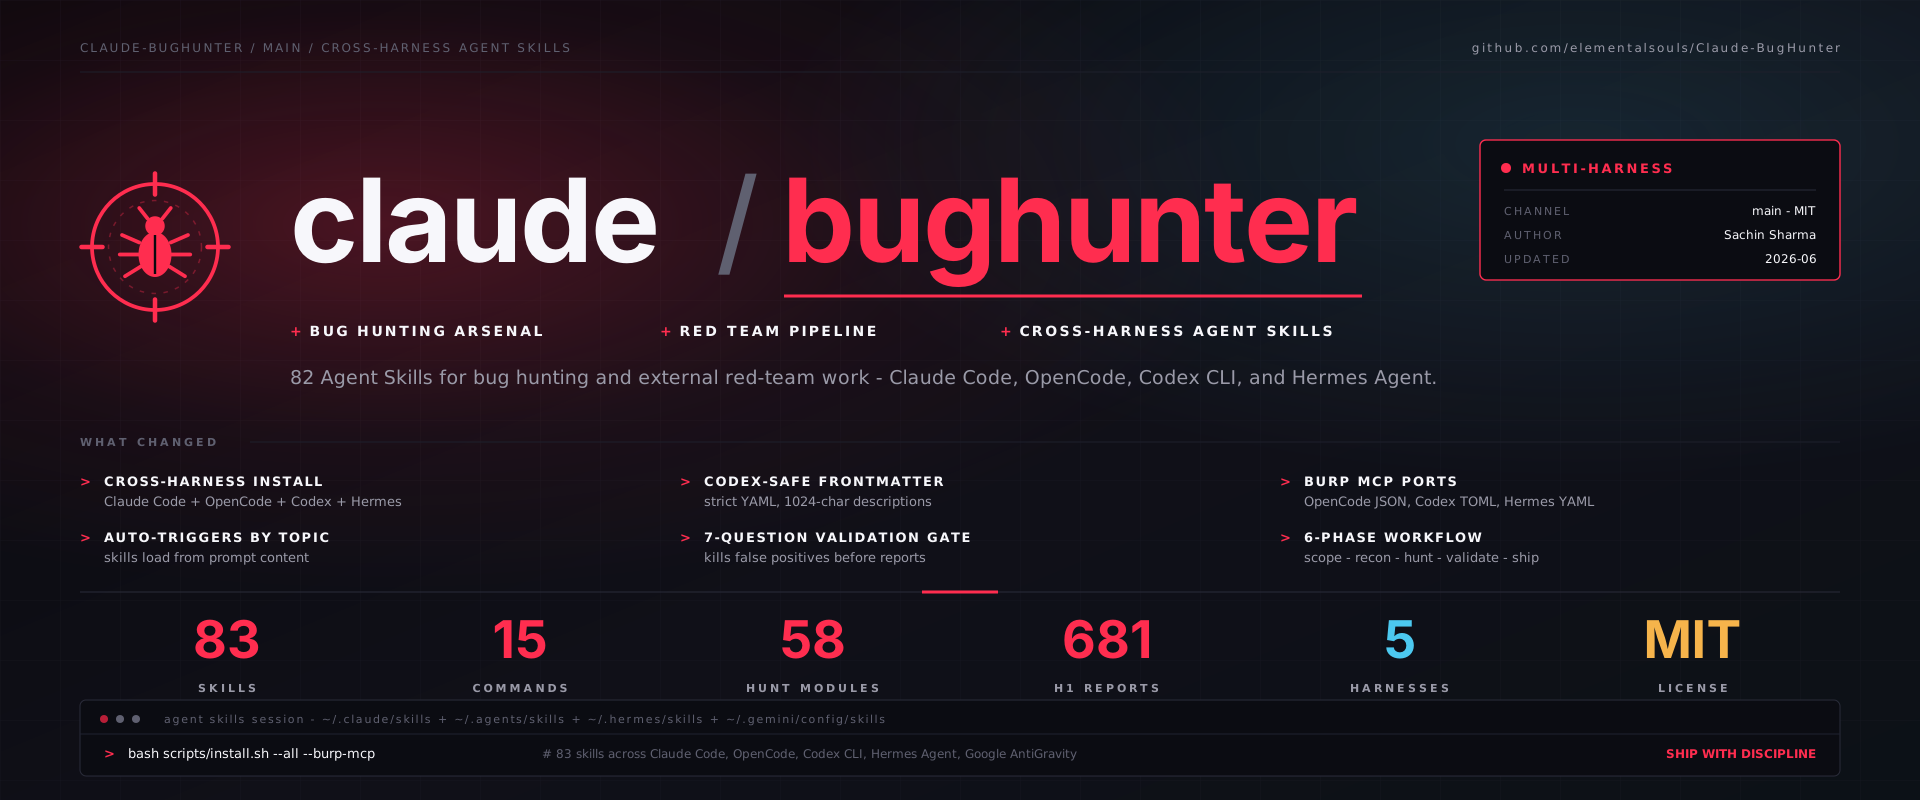
Claude BugHunter, which is currently ranked number one on GitHub Trending (with 126,000 stars), is a Claude Code skill pack designed for vulnerability discovery and external red team operations. It comprises 83 skills, 15 slash commands, and vulnerability patterns extracted from 681 publicly disclosed reports (433 of which are annotated with specific source references), covering 24 core vulnerability categories, along with an enterprise identity and infrastructure attack matrix.
今天 GitHub Trending 日榜第一(12.6 万星在读)的 Claude BugHunter 是一套为漏洞挖掘和外部红队工作打造的 Claude Code 技能包:83 个技能、15 个斜杠命令、681 份公开披露报告提炼出的漏洞模式(其中 433 条逐条标注了引用来源),覆盖 24 类核心漏洞,外加企业身份与基础设施攻击矩阵。
How it differs from a typical "safety prompt"它和普通「安全提示词」的区别
Most online security prompts are role-playing exercises consisting of a few sentences, but BugHunter breaks down 681 publicly disclosed HackerOne reports into structured testing patterns. Each type of vulnerability has detection characteristics, payload variants, bypass checklists, and exploit chain templates. Agents receive a methodology rather than a slogan.
58 hunt-* skills are organised by vulnerability category (24 major categories including SQL injection, SSRF, privilege bypass, IDOR, etc.). The corresponding skill is automatically loaded based on the description of what is to be tested, and there is no need to manually call it by name. It also comes with VRT vulnerability category mapping and platform CVE chain knowledge.
The practical toolkit is also complete: The engagement-folder scaffolding generates the test project directory structure with one click, and Burp Suite is integrated via MCP. The author claims to have refined it repeatedly on authorised red team projects and training platforms such as DVWA, OWASP Juice Shop, and Hacker101.
网上大部分安全提示词是几句话的角色扮演,而 BugHunter 把 681 份 HackerOne 公开披露报告拆解成了结构化的检测模式:每类漏洞有检测特征、payload 变体、绕过对照表和利用链模板,Agent 拿到的是方法论而不是口号。
58 个 hunt-* 技能按漏洞类组织(SQL 注入、SSRF、权限绕过、IDOR 等 24 大类),描述要测什么就自动加载对应技能,不需要按名字手动调用;另配有 VRT 漏洞分类映射和平台 CVE 链知识。
实战配套也齐:engagement-folder 脚手架一键生成测试项目目录结构,Burp Suite 通过 MCP 集成接入,作者声称已在授权红队项目与 DVWA、OWASP Juice Shop、Hacker101 等训练平台上反复打磨。
Two installation methods两种安装方式
It is recommended to use the Claude Code plugin system: Run /plugin install claude-bughunter@elementalsouls in Claude Code. All 83 skills and 15 commands are loaded under the claude-bughunter: prefix namespace. They are automatically updated when the plugin is upgraded, and files are not copied to ~/.claude/.
When it is inconvenient to use the plugin system, use copy installation: Download the skill pack zip from this page and unzip it. On Windows, run pwsh ./scripts/install.ps1; on macOS/Linux, run bash scripts/install.sh. The skills will be copied to ~/.claude/ (on Windows, it is %USERPROFILE%\.claude\) and the hunt scaffolding will be set up.
HackerOne account is optional: The API credentials requested during installation are only used by the HackerOne MCP to read your private projects and reports. You can leave them blank and still use the tool fully. Public searches, project scoping, and other MCP tools are not affected.
推荐走 Claude Code 插件系统:在 Claude Code 里执行 /plugin install claude-bughunter@elementalsouls,全部 83 技能和 15 个命令以 claude-bughunter: 前缀命名空间加载,升级插件时自动更新,不往 ~/.claude/ 里拷文件。
不方便用插件系统时走复制安装:下载本页技能包 zip 解压后,Windows 运行 pwsh ./scripts/install.ps1,macOS/Linux 运行 bash scripts/install.sh,技能会拷入 ~/.claude/(Windows 是 %USERPROFILE%\.claude\)并接好 hunt 脚手架。
HackerOne 账号是可选的:安装时问的 API 凭据只用于 HackerOne MCP 读取你的私有项目和报告,留空也完全可用,公开搜索、项目范围等 MCP 工具不受影响。
The compliance red line must be clearly defined first.合规红线必须先划清楚
All the content in this skill pack is aimed at authorised scenarios: your own systems, targets for which you have purchased authorisation, or public projects on platforms such as HackerOne/Bugcrowd. The repository incorporates "staying within scope" into its skill discipline – this is its biggest difference from general security tools.
Using it to scan unauthorised targets is illegal, so don't have any ulterior motives. If you want to get started with vulnerability hunting, it is recommended that you first go through the entire process on dedicated practice ranges such as DVWA and OWASP Juice Shop.
这套技能包的全部内容都面向授权场景:自己的系统、买了授权的目标、或 HackerOne/Bugcrowd 等平台的公开项目。仓库把「保持在 scope 内」写进了技能纪律——这是它与泛安全工具最大的区别。
拿它去扫未授权目标属于违法行为,别动歪心思;想入门漏洞挖掘,建议先在 DVWA、OWASP Juice Shop 这类专门的练习靶场上跑通全流程。
Note小提示
For webmasters, it can also be used as a defensive tool: it can be used to audit their own sites from an attacker's perspective, and the resulting report format is also based on real disclosure cases. The previously added official Cloudflare security-audit-skill focuses on defensive checks, while BugHunter focuses on the attacker's perspective. The two complement each other. The complete skill pack accompanying this article can be found via the download button above.
对站长来说它也可以当防御工具用:让它以攻击者视角审计自己的站点,产出的报告模式同样来自真实披露案例。之前入库的 Cloudflare 官方 security-audit-skill 偏防御检查,BugHunter 偏攻击视角,两者互补。本文配套完整技能包见上方下载按钮。
⬇ Download · 点击下载:Claude BugHunter v2.1 完整技能包(GitHub 仓库 zip)
含 83 skills + 15 斜杠命令 + scripts/install.ps1 安装脚本 · 仅用于授权测试
阅读与点赞数据保存在你的浏览器本地,欢迎留下你的想法。
 今日正能量学一点,用一点;今天种下的种子,会长成明天的能力。去免费下载专区 →广告
评论 文明发言,让讨论更有价值